Online PCAP analyzer & viewer
Free for sanitized captures. Private for incident, client, and internal traffic.
Analyze PCAP online: upload .pcap or .pcapng and inspect HTTP, DNS, credentials, files, and host relationships in minutes. No signup for public analysis. Use private plans for internal, client, or incident data.
Upload sanitized captures to evaluate the product. For captures with credentials, internal hosts, or incident evidence, use a private plan or the self-hosted PCAP analyzer. Need volume pricing? Talk to us →
Analysis Modes
Pick the mode that fits the capture
Use public analysis for sanitized PCAPs, private plans for sensitive data, and on-prem when captures cannot leave your environment.
Public analysis
Best for sanitized traces, product evaluation, labs, and quick checks where a public result page is acceptable.
- No signup required
- Upload and inspect results immediately
- 25 MB limit on free uploads
Private analysis
Use Packs or Workspace plans when the capture includes internal hosts, credentials, customer traffic, or active incident evidence.
Packs from $6.99 · Workspaces from $11.99/month
- Results stay out of the public feed
- Built for SOC, DFIR, and consulting teams
- Good fit for recurring teams and one-off sensitive cases
On-prem deployment
For regulated, air-gapped, or isolated environments where packet captures and evidence cannot leave your infrastructure.
- Keep PCAP inside your boundary
- Support restricted networks and evidence handling
- Runs in air-gapped and isolated networks
What You Get
A PCAP reader that finds the useful parts
The product is most valuable when it removes boring triage work: reconstructing sessions, finding credentials, extracting files, and mapping relationships between hosts.
Reconstruct HTTP Sessions
Inspect requests, responses, headers, forms, and transferred content without stepping through raw packets one by one.
Read more Show less
Use this to review suspicious web traffic, rebuild client-server exchanges, and move from packet capture to analyst-readable evidence faster.
When you need to verify form submissions, web payloads, or transferred documents, the session view gives you a shorter path than raw Wireshark drilling.
Map Hosts and Services
See which hosts communicated, which services were exposed, and where to focus next during triage.
Read more Show less
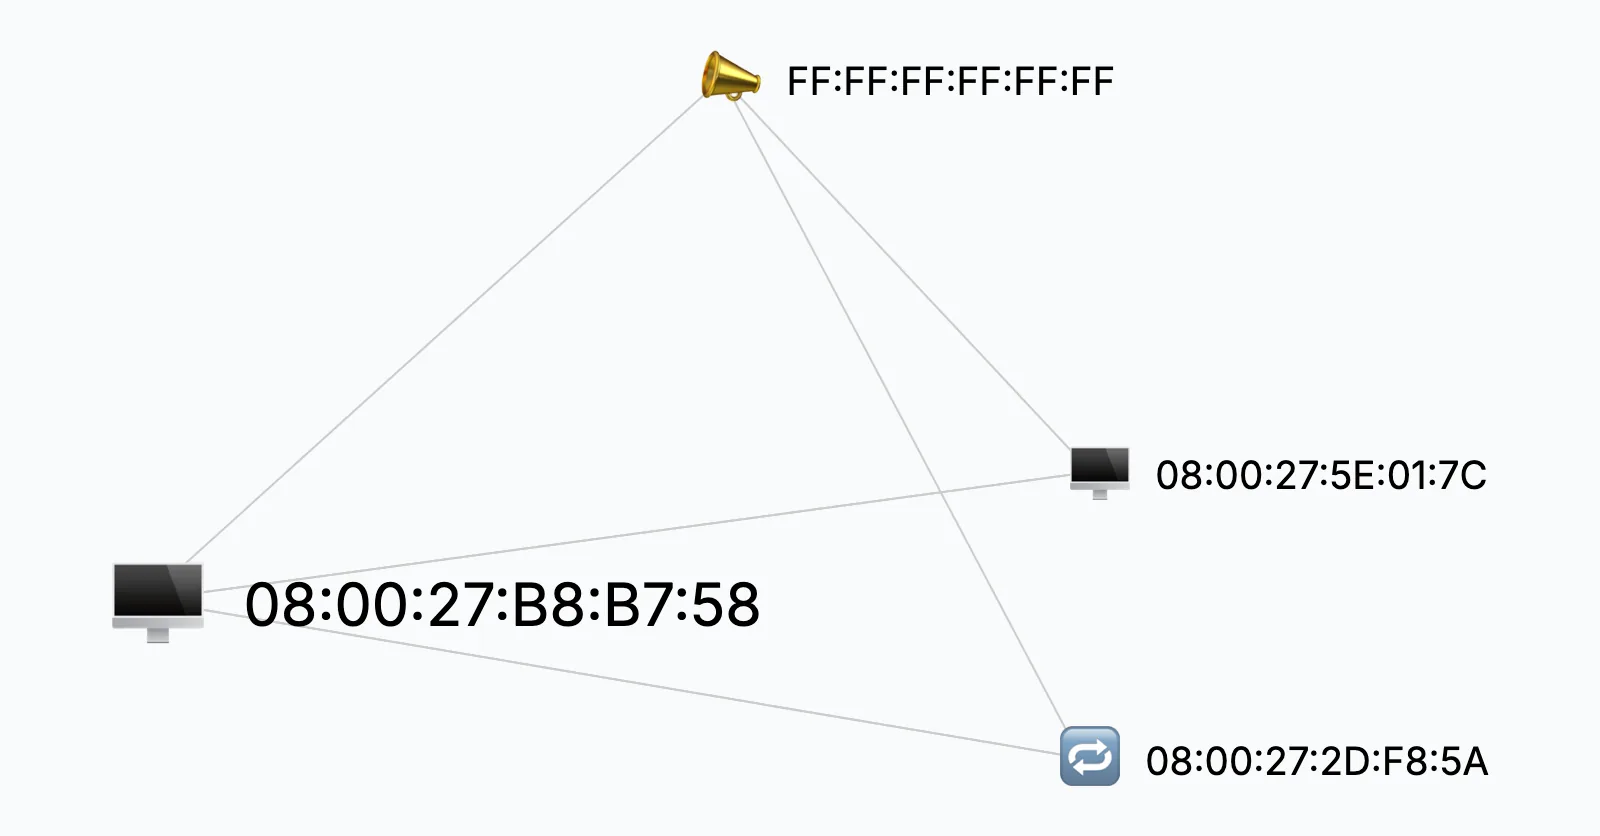
Classify nodes, review TCP and UDP communication patterns, and identify infrastructure roles from the capture itself.
Use passive fingerprints and protocol hints to spot DNS, DHCP, LDAP, and other service activity without building manual host inventories.
The graph view is useful when the question is not "what packet is this?" but "which systems were involved and how are they related?"
Review Wireless Artifacts
Extract SSIDs, probe requests, multicast patterns, and handshake artifacts from wireless captures.
Read more Show less
Use the wireless view to separate infrastructure noise from useful evidence and identify what access points and client probes were present in the trace.
Detected WPA/WPA2 handshakes can be exported to .hccapx for offline recovery
workflows with Hashcat.
Extract Files and Payloads
Pull images, documents, and transferred payload artifacts out of HTTP flows without rebuilding them manually.
Read more Show less
Use quick previews to confirm whether the capture contains useful artifacts before you spend time on deeper manual analysis.
This is especially useful for phishing reviews, malware delivery checks, or any case where the question is "what actually moved over the wire?"
Find Credential Exposure
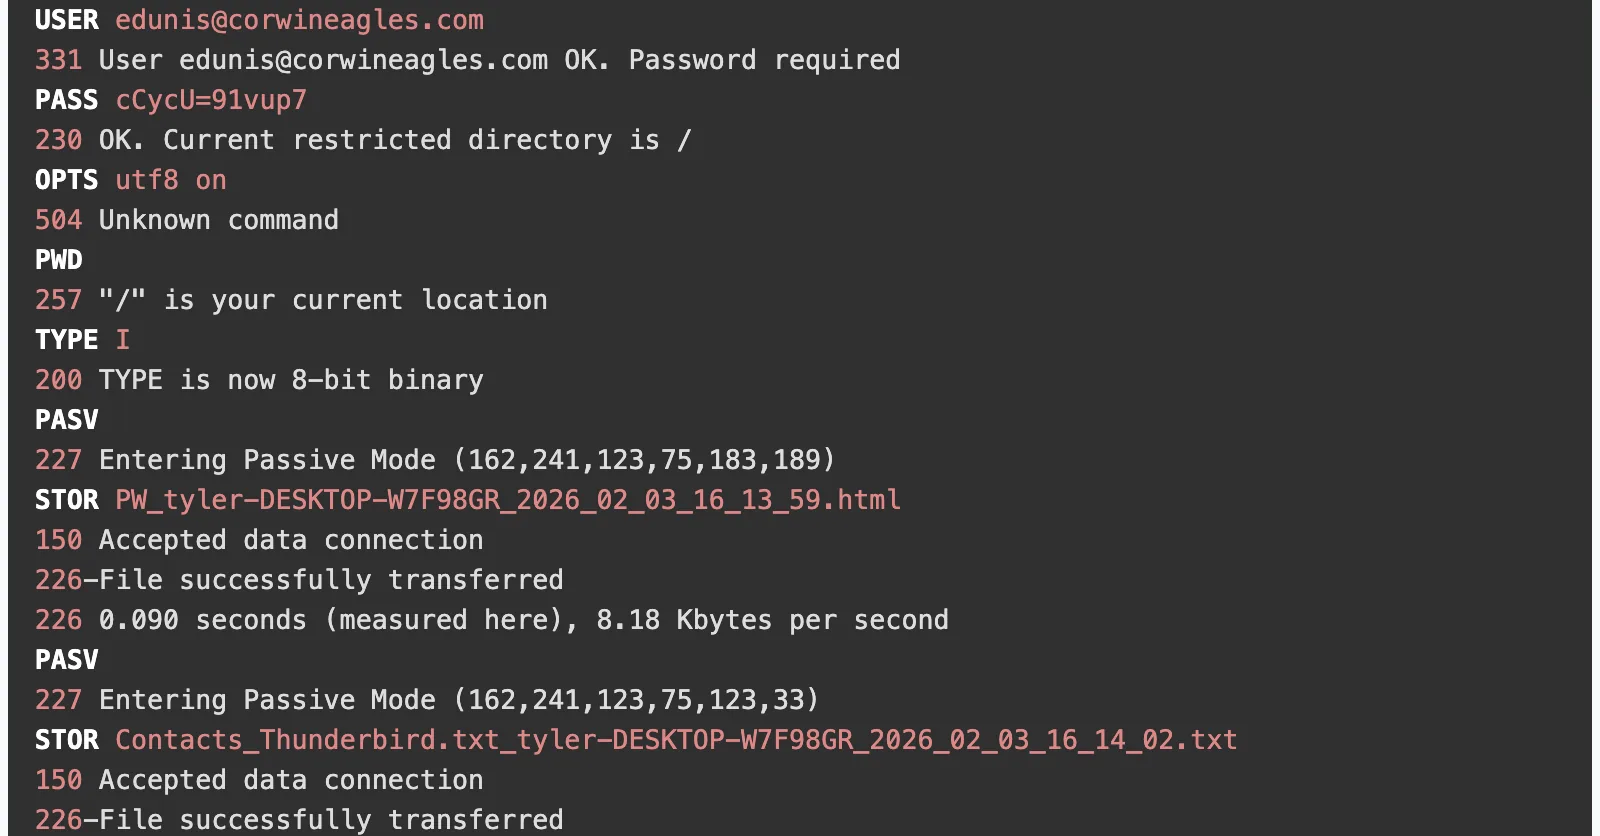
Scan the capture for plaintext credentials, auth material, and challenge-response artifacts across common protocols.
Useful for confirming whether a capture contains credential leakage worth escalating.
Read more Show less
The analyzer also looks for challenge-based authentication artifacts that may matter during DFIR and credential exposure reviews.
- HTTP Basic/Digest
- SIP Digest & SMB
- NTLMv1/v2
- Kerberos & LDAP
- Postgres & MSSQL
- Telnet/FTP
Spot Triage-Worthy Events
Identify suspicious patterns such as scans, insecure credential use, and other anomalies that deserve analyst attention.
Read more Show less
Event detection is useful when you want the product to highlight likely starting points instead of manually hunting through the full trace first.
For recurring team use, this becomes more valuable in private plans where sensitive captures and ongoing incident work should not sit in a public result feed.
Working with sensitive captures? See private plans → to keep results out of the public feed.
Use Cases
PCAP analysis use cases on real captures
Six tasks analysts bring to a packet capture, each worked through public sample captures: what A-Packets shows, how to confirm it in Wireshark, and what a capture cannot tell you.
-
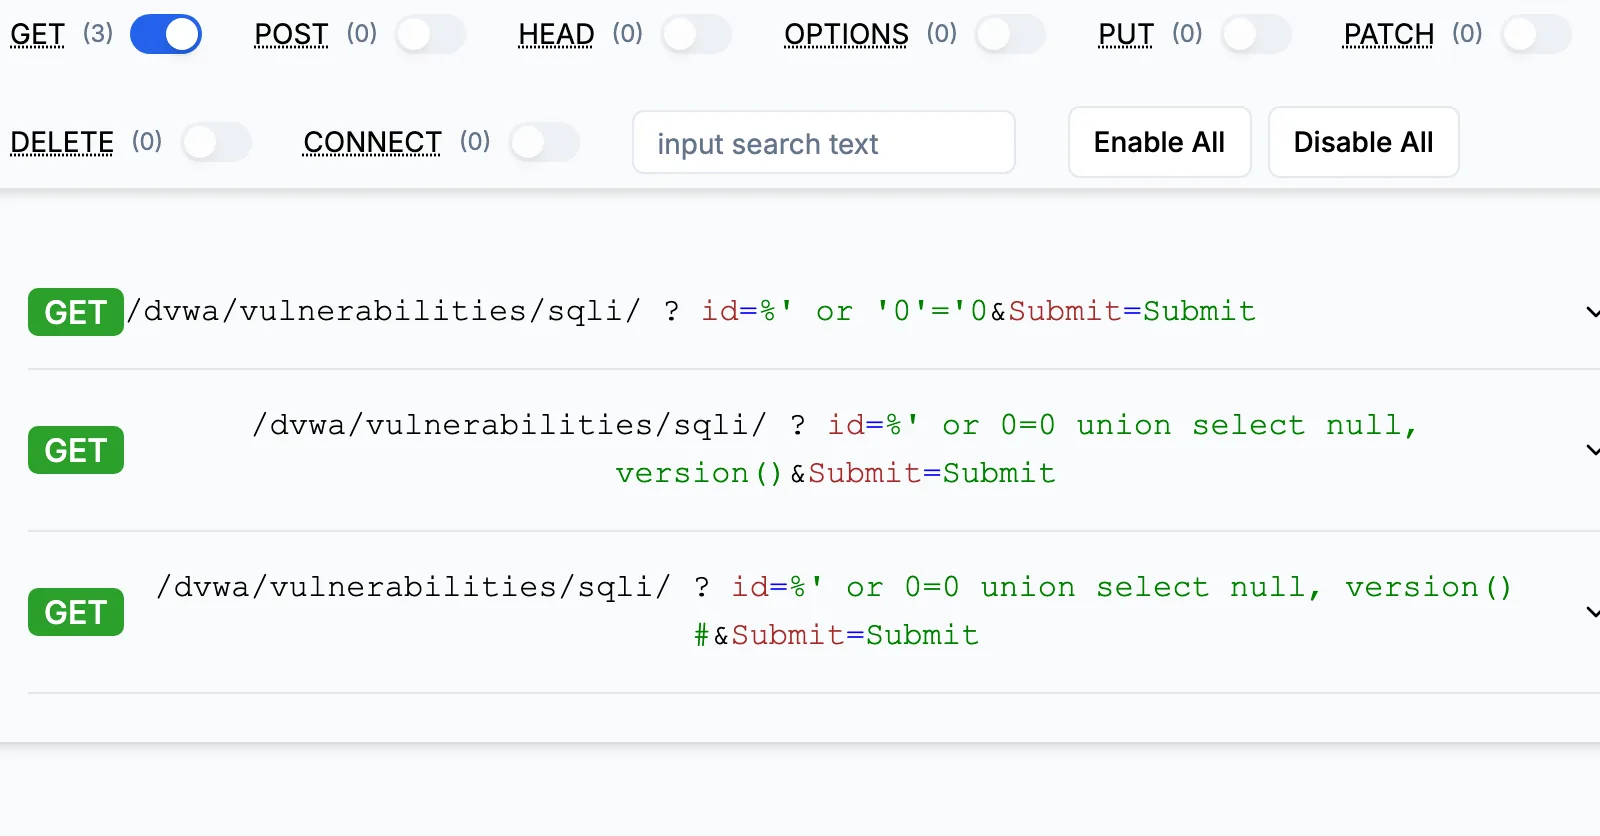
Viewing captures
Open a PCAP file online
Open a pcap or pcapng file in the browser without Wireshark, find the view that answers your first question, and share the result safely.
-
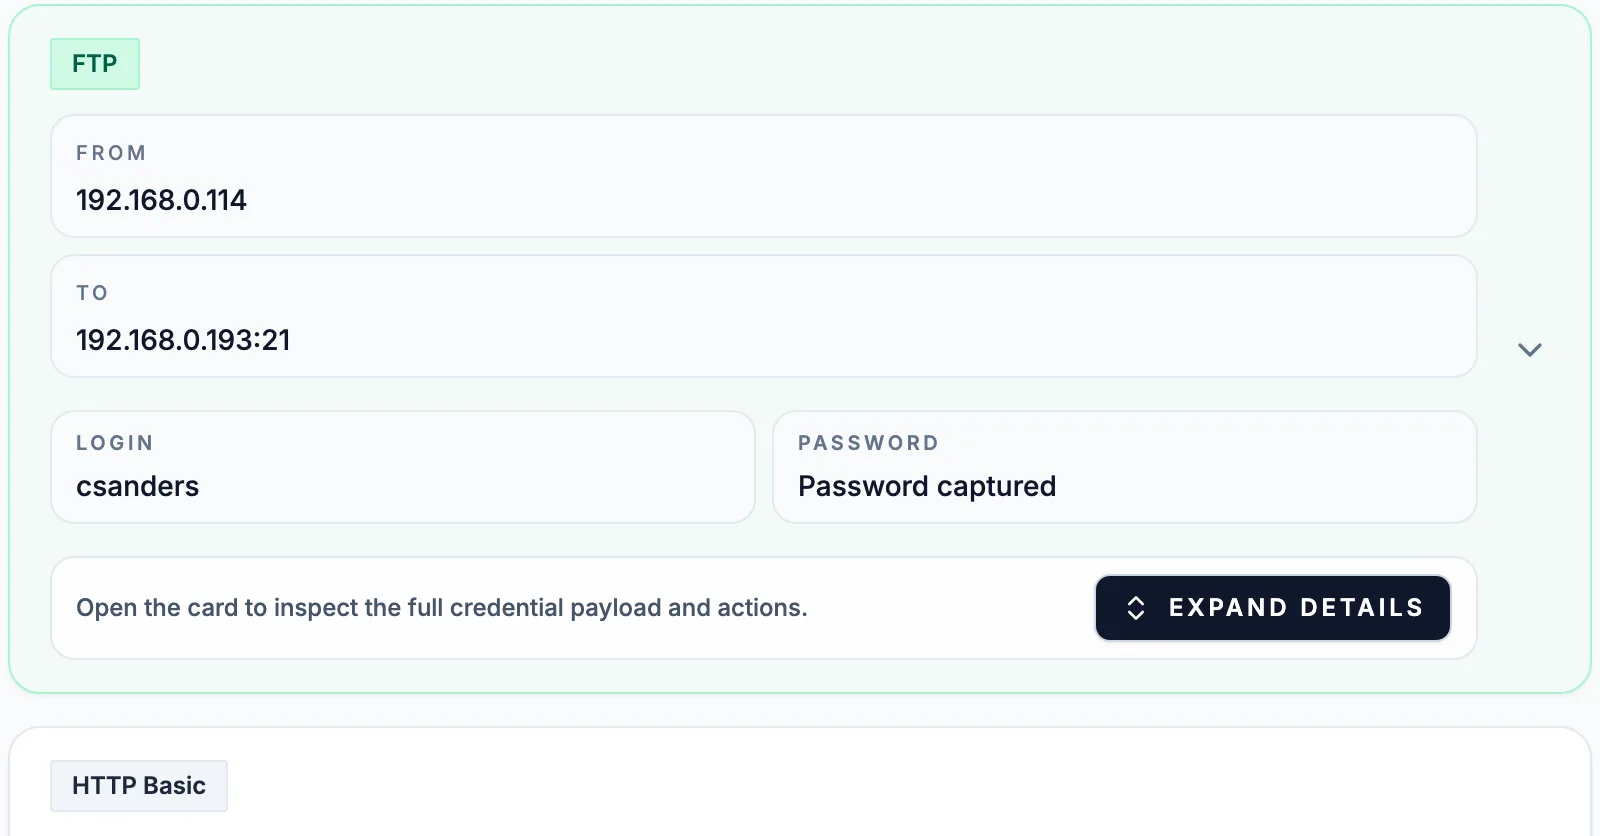
Credential exposure
Cleartext password audit
Run a cleartext password audit from packet captures: where to capture, what counts as exposed, a fix for each protocol and the retest.
-
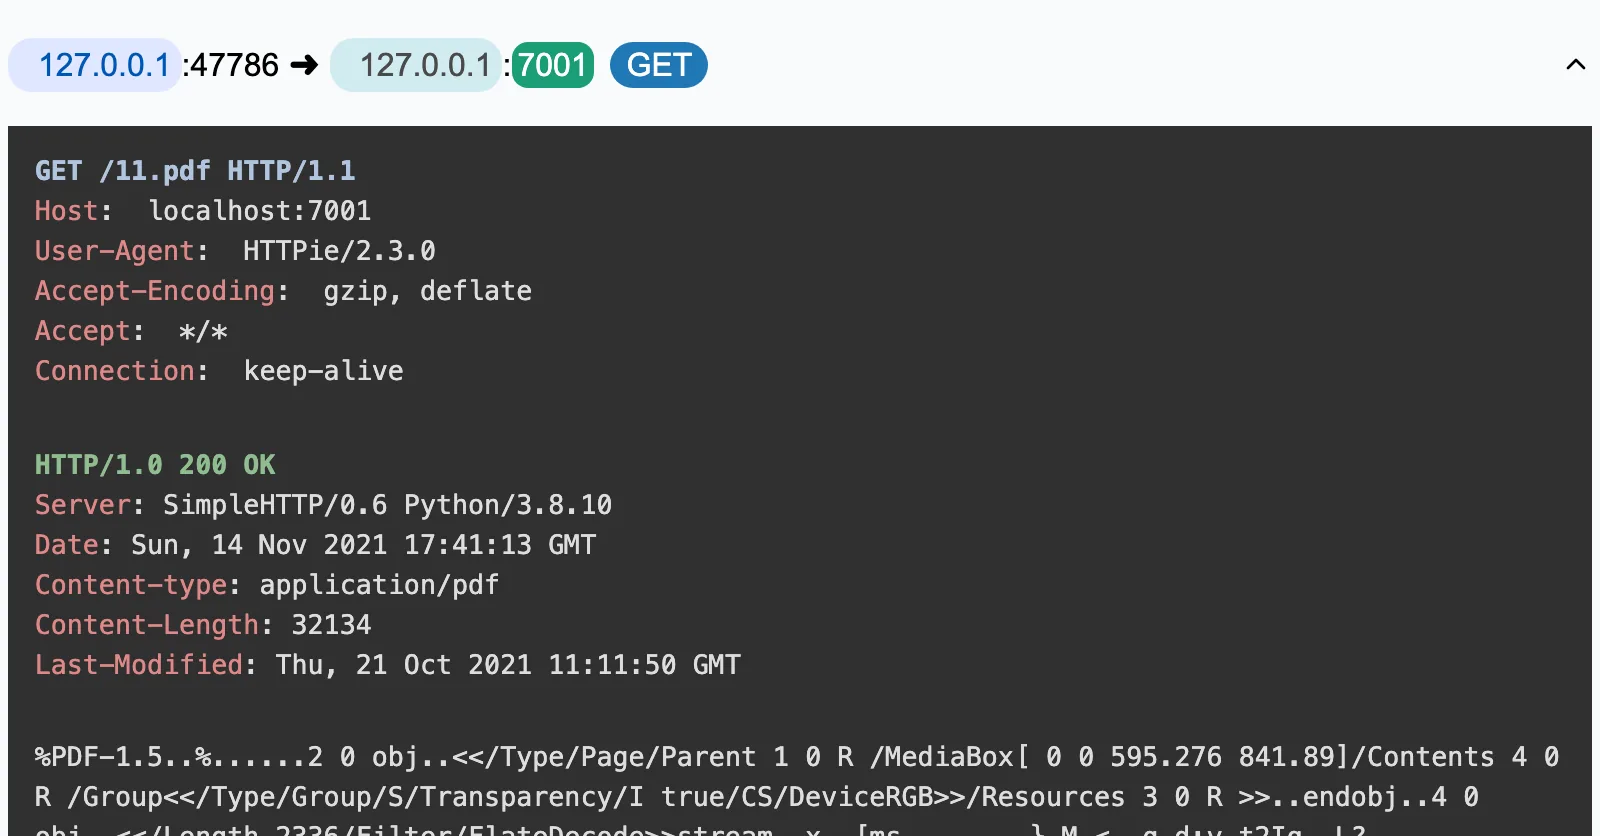
File carving
Extract files from a PCAP
What a capture can give back: files carved from HTTP, what needs Wireshark's export, what TLS seals, and how to keep each file's origin.
-
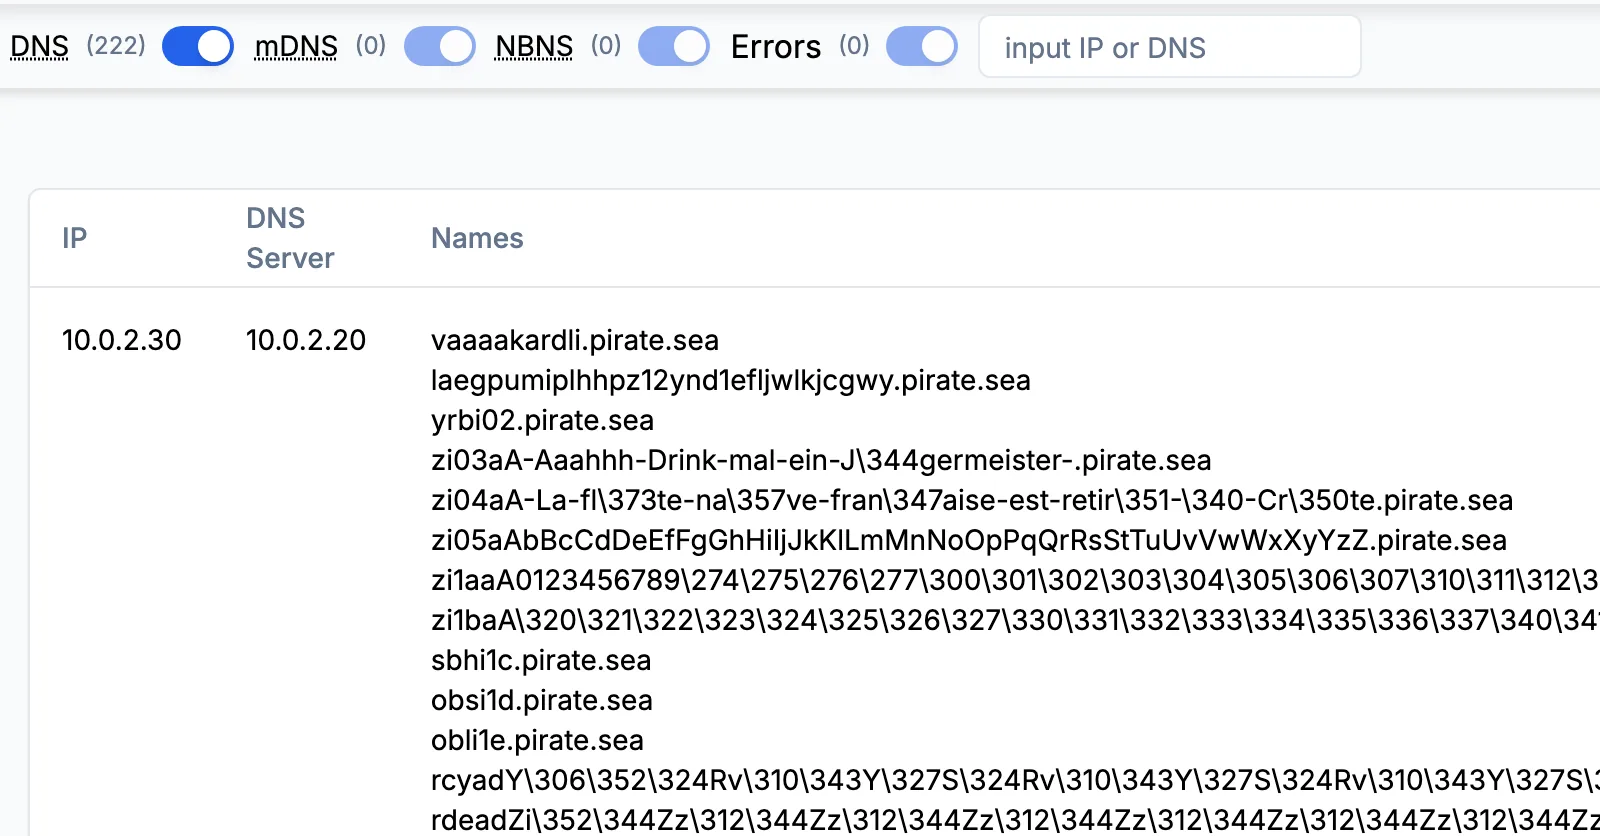
DNS
DNS tunneling in a PCAP
Tell a DNS tunnel from a subdomain sweep and ordinary lookups with four sample captures, the DNS view and three tshark counts.
-
Layer 2
ARP spoofing in a PCAP
Two ARP poisonings that leave very different traces, one false alarm, and the checks in A-Packets and Wireshark that catch both.
-
Incident response
Malware traffic analysis
Triage an infected host across five malware families: the arrival, the command channel, what left the network and what to hand over.
Online PCAP analyzer FAQ
The main questions are usually about privacy, public vs private analysis, and what the free mode is actually for.